AI now finds holes faster than you can patch them. Find yours first.
“I think 10 days is too long. These things [are] going to happen much faster than every 10 days.”
The Self-Audit Kit: 40 prompts and a step-by-step playbook to audit your vibe-coded app in a weekend.
$99 at launch. Founder price $49 for the first 50 waitlist members who buy.
21 October: what one AI-found flaw did in a day
- August. Researchers using AI crack a PHP flaw that had been known for years but was "too hard" to exploit. Rated 9.2 out of 10.
- Days before the fix. Details leak. Nobody knows how.
- 21 October. The patch ships a day early. AWS reports a jump in attacks and Cloudflare sees millions of attempts within hours.
- Same day. Governments across Europe take sites offline. The NSA and FBI issue warnings.
The sites that got hit weren't the clever ones. They were the ones nobody had checked in years. Once a fix is public, attackers read it like a map and go looking for everyone who hasn't applied it.
Your app isn't PHP. It's worse off: written fast, by AI, and never audited by anyone.
Source: All-In Podcast, 23 Oct 2026.
What's in the kit
- Copy-paste prompts for Cursor and Claude Code in 8 categories: secrets and keys, IDOR, API auth, security headers, GDPR, contact forms, RLS, dependencies
- An audit playbook in the order I run it, with what a pass looks like and how to fix a fail
- Video walkthroughs: me finding and fixing each problem in a deliberately broken Next.js + Supabase app
- Updates as the tools change. Buyers get an email each time
Works on Vite and Express too. Each prompt notes where the stacks differ.
On 24 to 26 October I rotated every key I own
On 20 October, attackers got into Railway, the platform that runs my app's backend. They were hunting for AI API keys, and Railway told every customer to rotate theirs. I didn't know what had been exposed, so I treated it all as exposed: database keys, payment keys, signing keys, the lot. Then I went through my own app line by line.
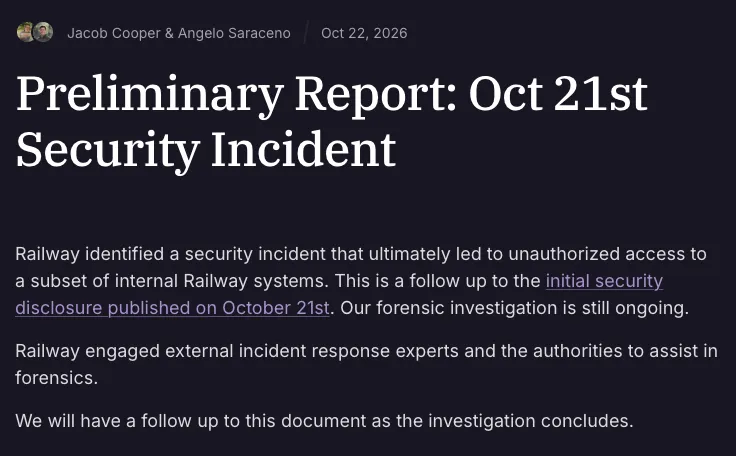 Railway's preliminary report, 22 Oct 2026 (opens Railway's blog)
That process is this kit. It's the same audit, in the same order, written so you can run it on your app without being a security engineer.
I'm the person behind @TheLazyDeveloper (22.5K on TikTok). My security videos are the ones people share most: database security, security headers, GDPR. This is the process behind them.
Is the course still free?
Yes. Every lesson and guide on the site stays free. The Kit is an optional toolkit for people who've shipped something and want to check it properly.
Find the holes before someone else does
$99 at launch. Founder price $49 for the first 50 waitlist members who buy. In return, tell me what you want to learn next.